

About members in LaunchDarkly
Account members are people who work at your organization or have access rights to your organization’s LaunchDarkly environment for another reason, such as contractors or part-time employees.LaunchDarkly account members are not LaunchDarkly usersLaunchDarkly users are people who encounter feature flags in your app. In many cases, they are customers or people accessing your product. Users are represented by user “contexts.” Contexts can also represent other entities encountering feature flags, such as devices, organizations, and more. To learn more about contexts, read The Contexts list.
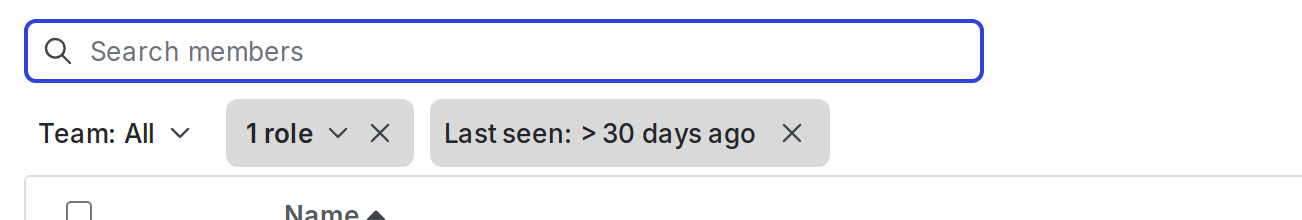
The "Members" tab with filters applied.
- N minutes/hours/days/months/years ago: The amount of time since a member last logged in. If a member logged in using the API, the status also displays the name of the personal access token they used.
- No data: The member has never logged in.
Add members to LaunchDarkly
The Members list is an Admin-only featureThe Members list is only accessible if you have a LaunchDarkly Organization admin role, or an Admin or Owner base role, or another role that allows a member action. To learn more, read About member roles, below, and Member actions.
- Click the gear icon in the left sidebar.
- Click Members. The Members list appears.
- Click Invite members. The “Invite members” panel appears.
- Enter one or more email addresses in the Email addresses field. Separate addresses with commas or line breaks.
- (Optional) Choose an Organization role. This role provides access to organization settings, such as members, teams, and integrations.
- (Optional) Choose one or more teams from the Assign members to teams menu. Members inherit project permissions from the teams they are assigned to.
- (Optional) Choose one or more roles from the Project access menu. These roles assign project permissions directly to the members, across all projects in your organization.
-
(Optional) If a role you chose defines a role attribute, enter one or more resource keys in the Resource keys field. The resources you enter apply in place of the role attribute. For example, if a role defines a role scope with a role attribute of
developerProjectKeys, enter the keys of the projects these members should have access to. To learn more, read Set role attribute values. -
Click Invite.
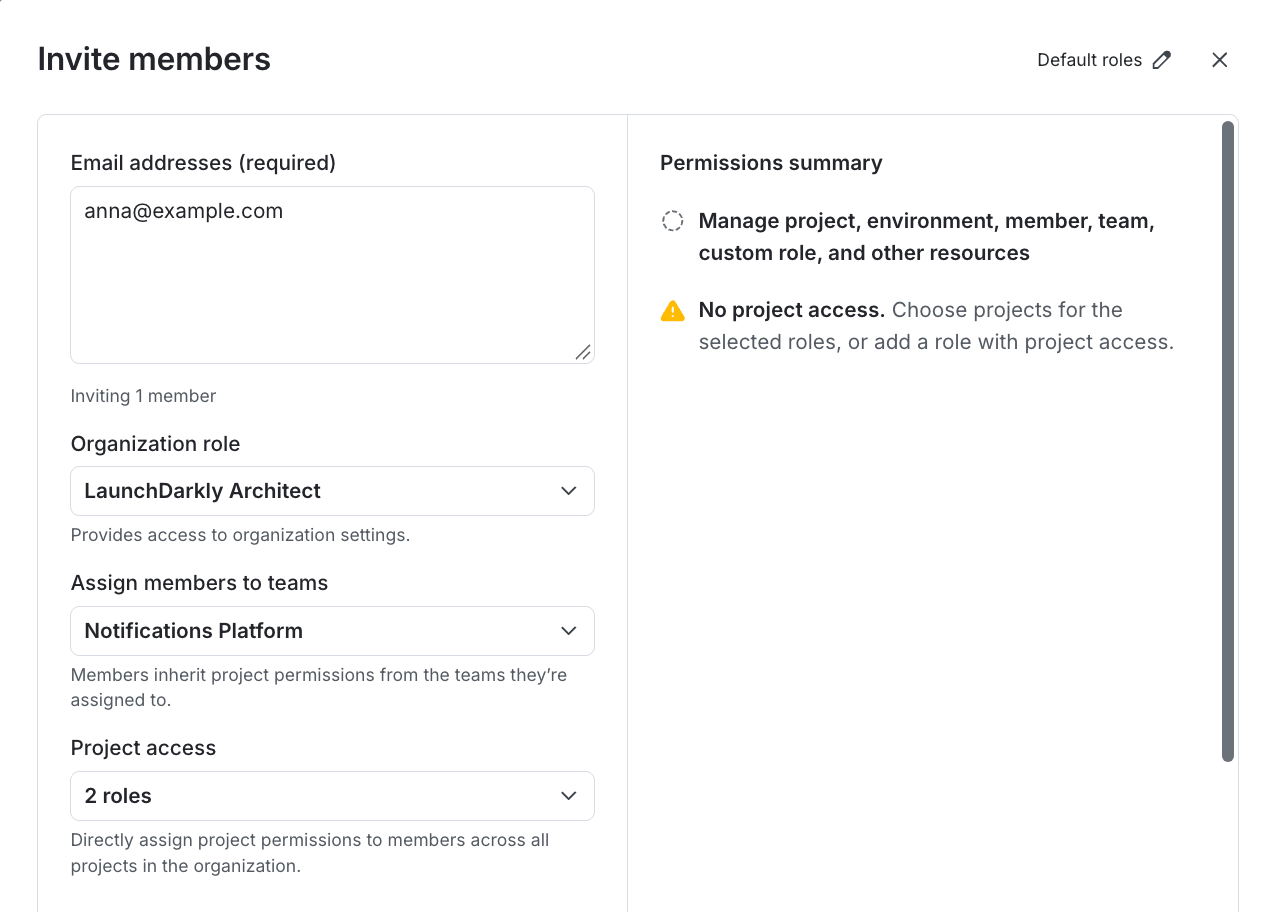
The "Invite members" dialog.
Members with an organization role but no project accessIf you choose an organization role but do not assign any teams or project access, the members you are inviting will have administrative access only, with no access to any project. Those members can reach your organization settings but cannot access your flags or other resources.To give them project access, assign a team, a project role, or both.
Invite members using classic roles
The invitation panel assigns an organization role and project roles separately. If your organization still relies on the base roles, you can switch the panel to assign one of those instead. To use classic roles for an invitation:- Click Default roles in the “Access” section.
- Select Classic roles.
- Choose a Member role.
- (Optional) Choose one or more teams in the Assign members to teams field.
- Click Invite.

You can also use the REST API: Invite new members
Accept pending requests
You can also allow people in your organization to find and request to join your LaunchDarkly account themselves. To learn how, read Organization access settings. When someone in your organization requests to join your LaunchDarkly account, the LaunchDarkly Organization admins and Owner receive the request in an email, and the pending request is available for approval on the Members page. To accept a pending request:- Click the gear icon in the left sidebar to view Organization settings.
- Click Members. The Members list appears.
- Click Pending requests. The “Manage pending requests” dialog appears.
- Check the checkbox next to the members you wish to add to your LaunchDarkly account.
- In the “Role” column, select the role that each member should have.
- In the “Request status” column, click Accept.
Export a list of members
You can export a list of your account members to a CSV file. The file includes their IDs, email addresses, first and last names, and roles. Here’s how:- Click the gear icon in the left sidebar to view Organization settings.
- Click Members. The Members list appears.
- (Optional) Filter by Team, Role, or Last seen if you want to export a subset of your account members.
- Click Export CSV. A CSV file of account members downloads to your machine.
You can also use the REST API: List account members
About member roles
You can assign different roles to LaunchDarkly account members. LaunchDarkly provides several roles which include access to common sets of features. To learn more, read Managing roles and Managing roles assignments. Customers on select plans can create additional roles to more specifically define the actions members can and can’t take. You can give an account member a role you’ve created in two ways: by giving the role to the member, or by giving the role to a team and adding the member to that team. To learn more, read Roles and Managing roles.Enable multi-factor authentication
For additional security, you can require multi-factor authentication (MFA) for your LaunchDarkly account. When MFA is enabled, account members won’t be able to log in to the LaunchDarkly user interface without verifying their identity with a second method. We strongly recommend that all LaunchDarkly members enable MFA for their individual accounts, and that administrators enforce MFA for their entire organization. In the event of a credential leak or device theft, MFA can prevent malicious third parties from accessing a LaunchDarkly account they should not be able to access. To learn more, read Multi-factor authentication.Remove members from LaunchDarkly
To remove a member from your account:- Click the gear icon in the left sidebar to view Organization settings.
- Click Members. The Members list appears.
- Find the member in the list of account members.
- Click the member’s name.
- Navigate to the Settings tab for that member.
- Click Delete member.
- They are removed from being a flag maintainer.
- Their personal access tokens are deactivated. Any service tokens that they created remain active.
You can also use the REST API: Delete account member